Identity
SSO maps each user to their role, department, and policy set across Teams, Slack, the web app, and mobile.
Inspection and PII controls
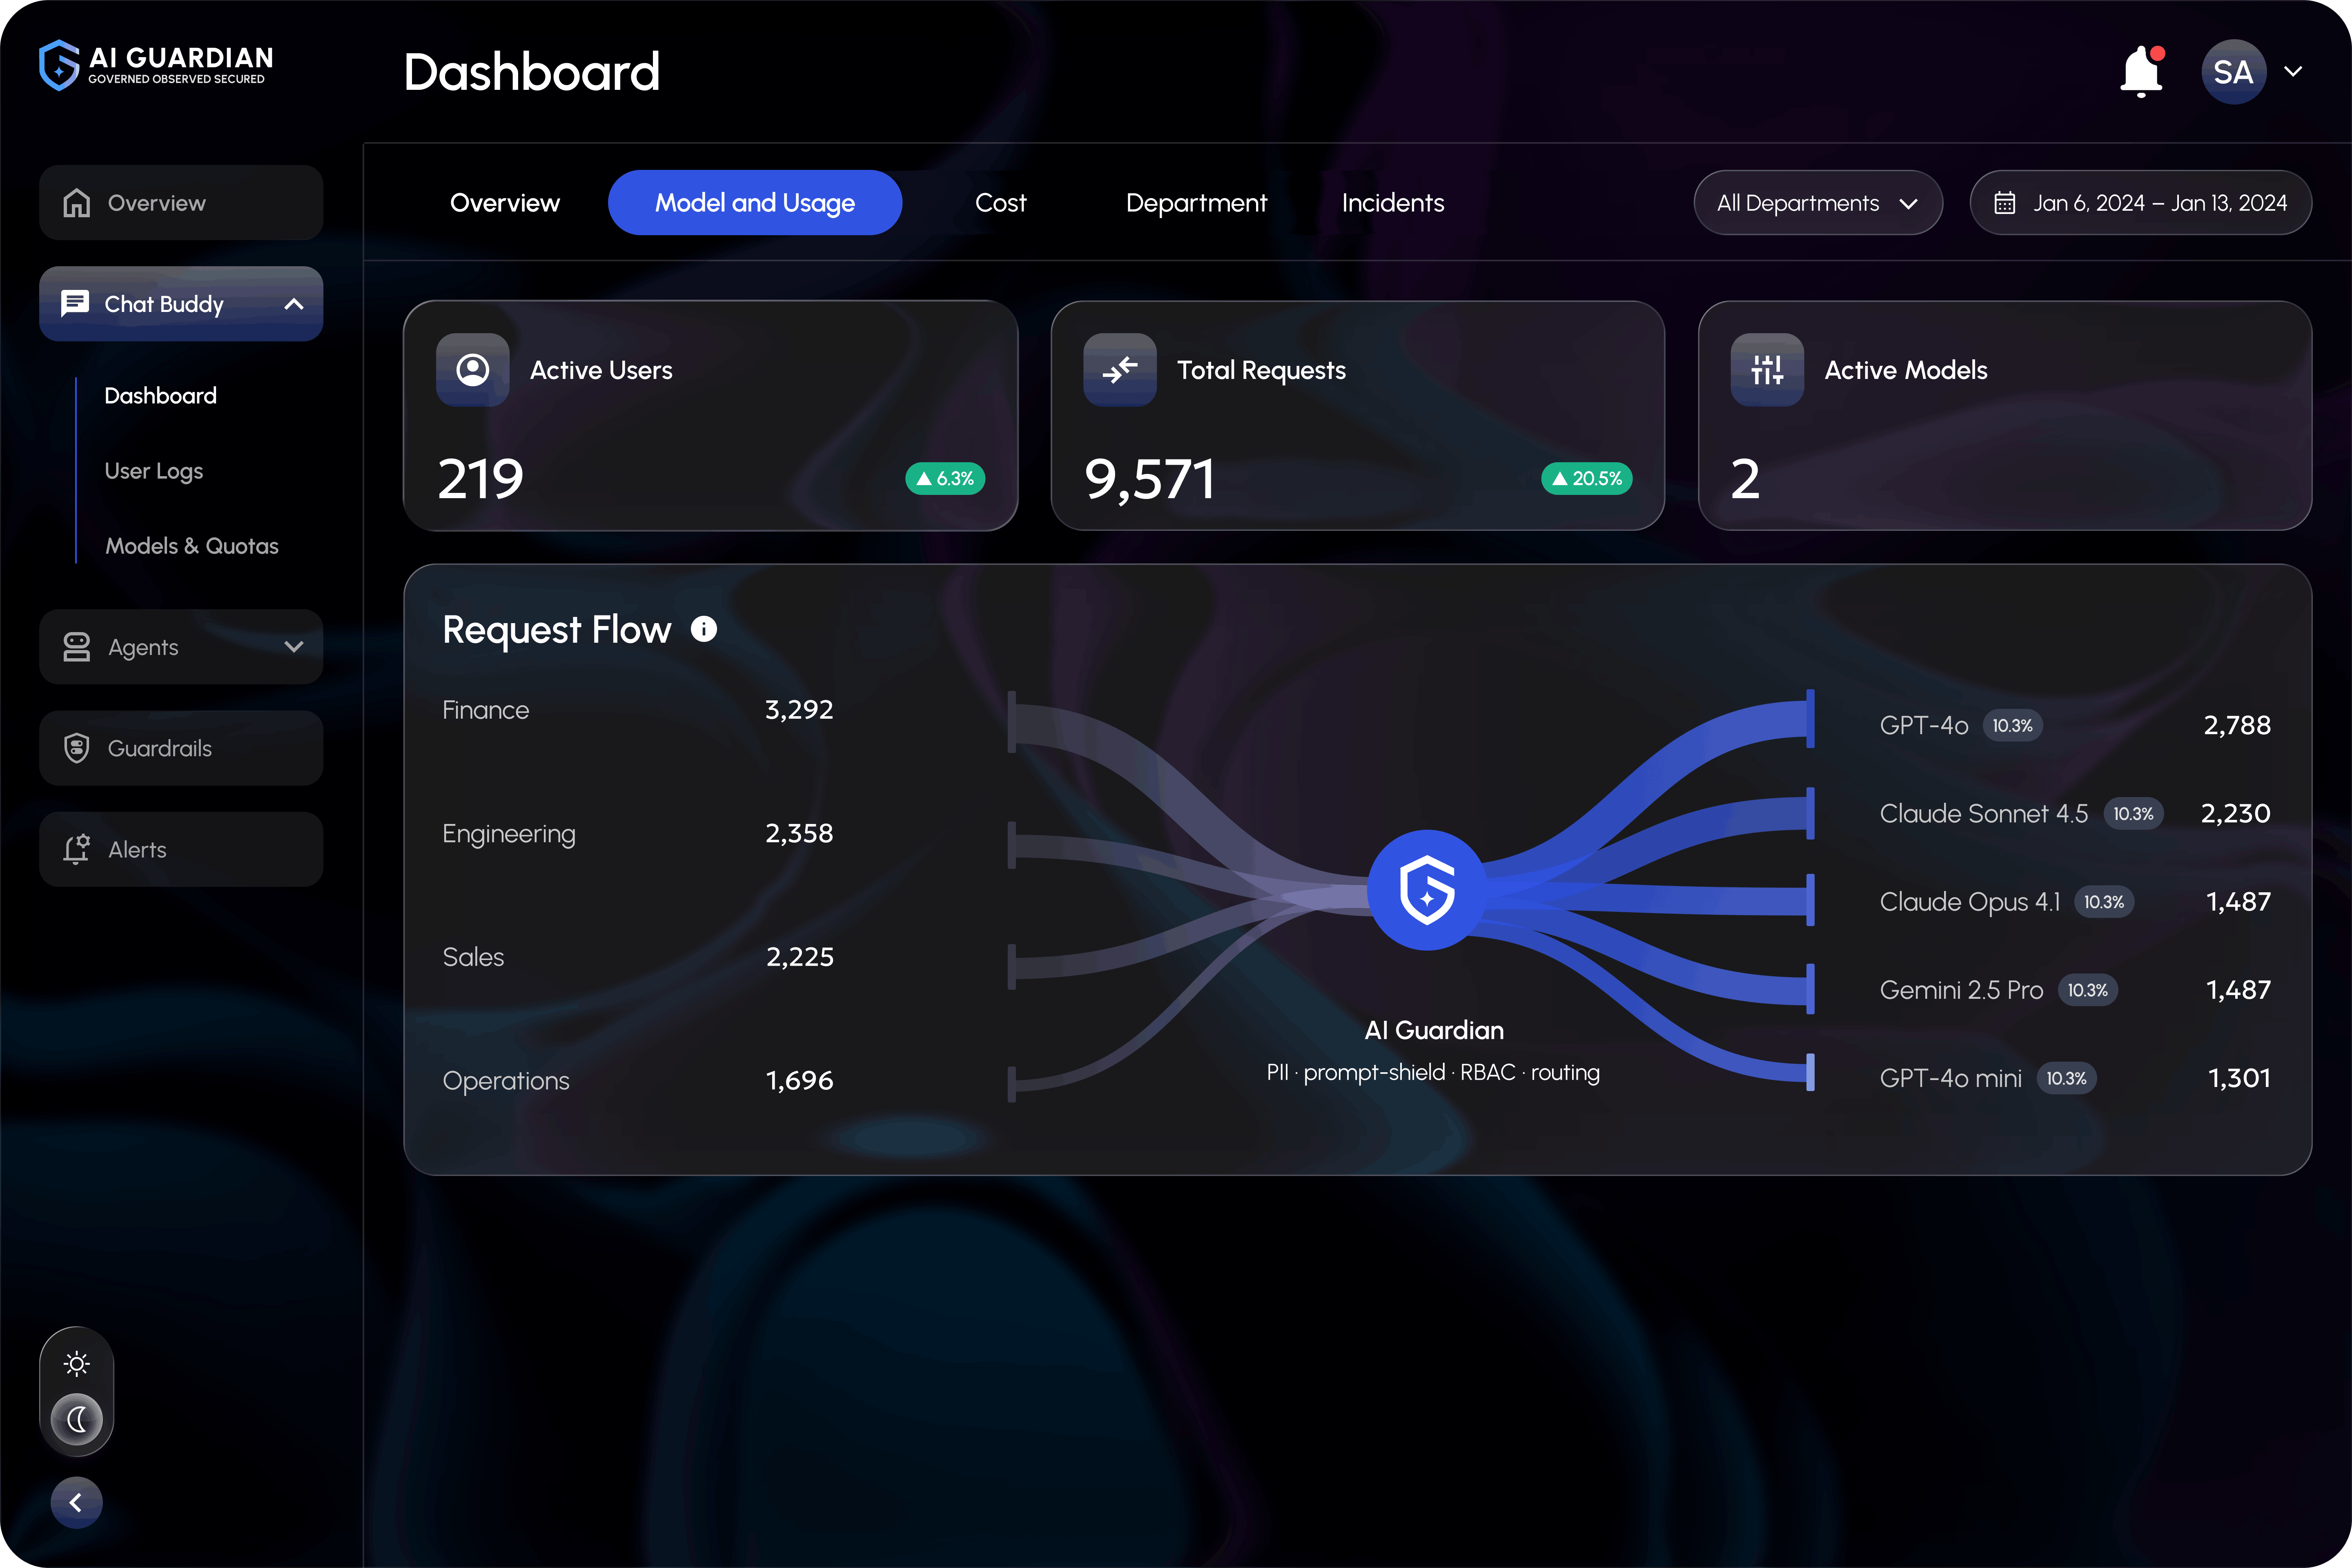
Prompts and attachments are scanned for PII, secrets, and prompt injection attempts. IBANs, national IDs, and financial details are masked before the request reaches any model.
Policy enforcement
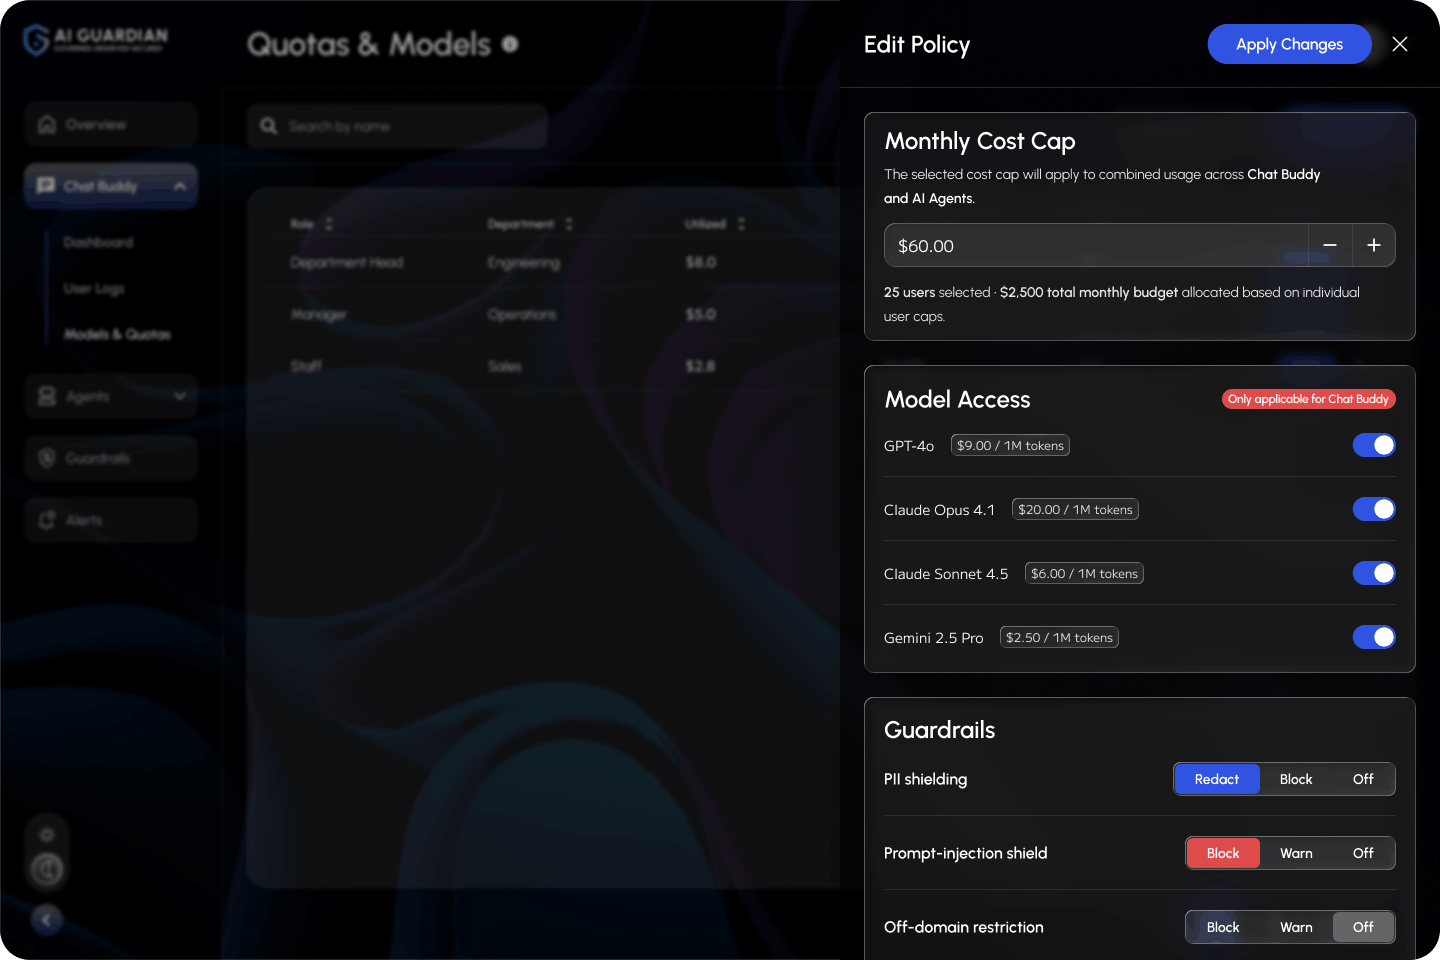
Off-domain requests are declined, and content rules are applied consistently across every approved model and agent.
Model routing and spend controls
Requests are routed to the right model based on role, task type, and available quota. Routine work goes to cost-efficient models; complex reasoning gets frontier capacity.
Agent registry
Custom and third-party agents connect through a central registry, inheriting the same identity, redaction, spend, and audit controls as any standard prompt.
Audit and executive visibility
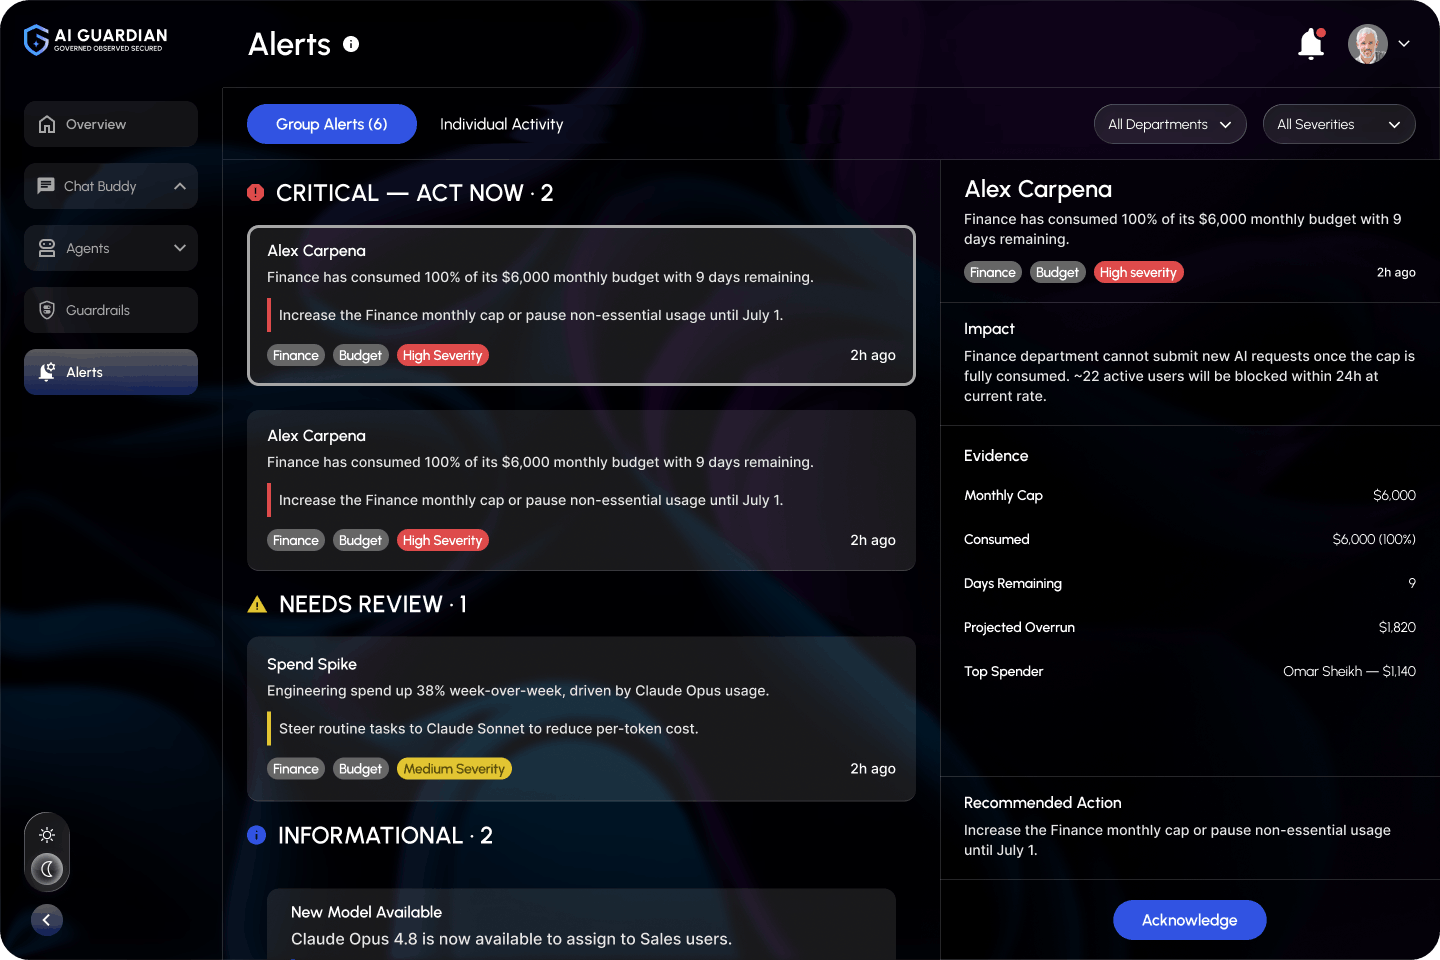
Every response generates a trace covering identity, policy decisions, model used, tokens, and cost. Department heads manage local quotas; risk leaders see org-wide usage and blocked events.
AI Guardian deploys inside the customer's own Azure, AWS, or GCP environment. Prompts and logs stay within the tenant.
AI Guardian governs requests at runtime. It does not replace model-level bias testing or drift monitoring, and it can feed evidence into a program platform if you run one.