AI Governance Software
Engineered to Make Company AI Safe to Scale.
AI Guardian is AI governance software that gives every employee one approved path to AI, while every prompt, document, agent, model, and business action passes through the same identity, policy, security, cost, and audit controls. Deploy the AI governance platform in your own cloud, connect Teams, Slack, web, and mobile, and govern AI usage in days.
Same-day response · Final pricing confirmed in your consultation · Folio3 is ISO 27001 certified · Listed on Microsoft Marketplace
Microsoft Teams, Slack, Web App, Mobile, approved LLMs, internal agents, company knowledge, and business actions, all governed together.
See How AI Guardian Governs Enterprise AI in Real Time.
Watch how identity checks, pre-ingress PII scrubbing, fit-for-purpose model routing, and audit logging protect company workflows without adding employee friction.
Stop Choosing Between Speed and Control.
Restricting AI outright drives usage into the shadows. Ignoring it expands organizational risk. AI governance software gives employees a useful way forward without giving IT, Security, Finance, or Risk less control.
Shadow AI Is Already Here.
Personal accounts, unapproved tools, sensitive uploads, fragmented subscriptions, and missing audit evidence leave most organizations unable to see how AI is actually being used. Shadow AI detection software only solves half the problem, since seeing unapproved usage does not give employees a better option.
- Identity MatchSSO
- Prompt + File InspectionPII
- Policy-Based RoutingRoute
- Agent OrchestrationAgent
- Audit LoggingTrace
One governed path. Every AI interaction.
Before a request reaches a model, company knowledge base, agent, or business system, AI Guardian verifies identity, enforces policy, masks sensitive data, routes the request, and logs the outcome. It is one AI governance solution in place of separate proxies, filters, and spreadsheets stitched together.
Five controls run inside the enterprise AI governance platform before the answer comes back.
A single employee request moves through identity, data protection, policy, model routing, agent execution, and audit logging, without forcing the employee to manage the complexity.
Start where employees already work.
The employee asks a question or uploads a file inside Microsoft Teams or the AI Guardian Web App. SSO matches the user to their role, department, and policy set.
Inspect data before it leaves.
The gateway scans prompts and documents for PII, secrets, prompt injections, and off-domain compliance violations before the request reaches an external model.
Choose the approved model automatically.
Policy verifies departmental quotas, user permissions, and model access before routing the request to the approved LLM for that role and task.
Let governed agents do the work.
When needed, specialized agents collaborate, retrieve company knowledge, and execute approved API actions while inheriting the same identity and security controls.
Return the answer with evidence.
The sanitized response is delivered to the employee while token usage, cost, policy decisions, model activity, and the identity-attributed conversation trace are logged.
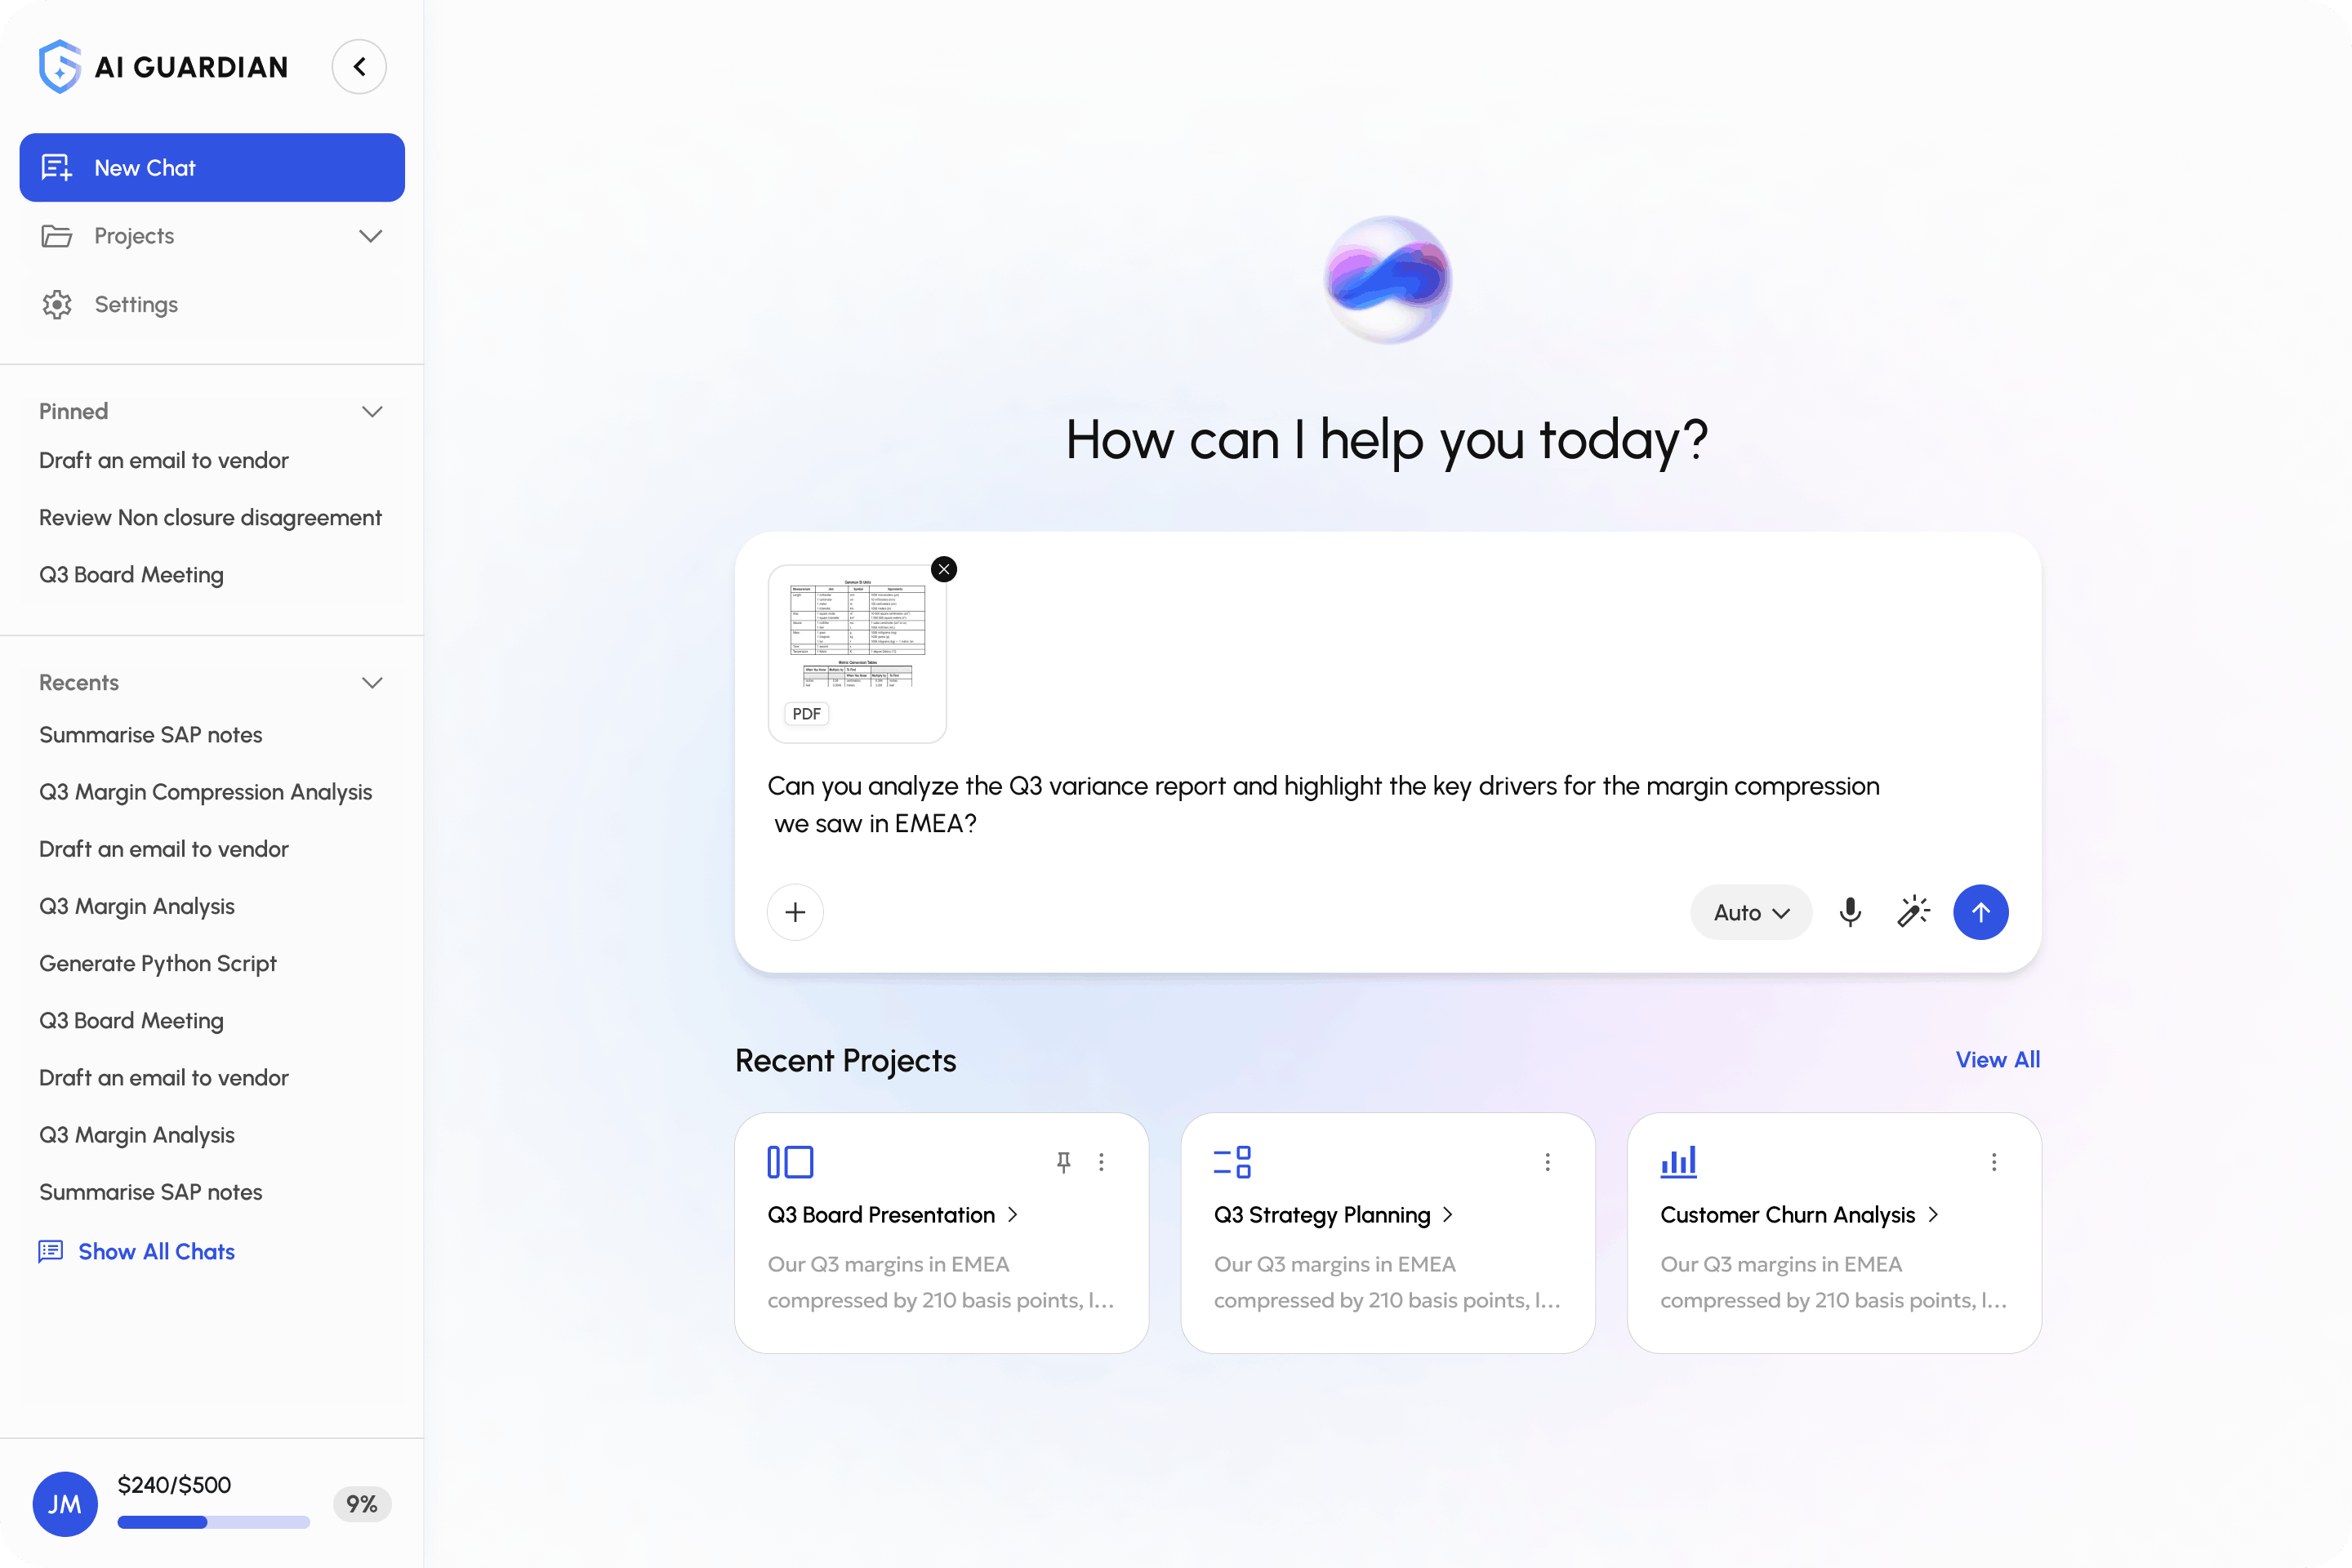
Ask AI Guardian
Review this vendor agreement and identify anything that conflicts with our procurement policy.
Policy checks completed. Sensitive identifiers masked. Full identity and cost trace logged.
Everything An Enterprise AI Governance Platform Needs, Already Built In.
Gateway routing, orchestration, data protection, governance, audit, security, and deployment run as one system, so nothing has to be re-integrated as usage grows.
One enterprise AI governance platform, seven layers deep.
Route every request to the right model, every time.
Multi-provider access with policy-based routing, automatic fallback if a provider fails, and caching and rate limits to keep performance predictable under load.
Run fixed workflows or let the platform plan the response.
Deterministic workflows handle repeatable processes on demand or on a schedule, while smart, AI-planned orchestration routes open-ended requests through the agent registry.
Catch sensitive data before it ever reaches a model.
PII is redacted at the point of capture, prompt-injection attempts are shielded, secrets are blocked from leaving the tenant, and content moderation runs on every request.
Give admins and department heads their own controls.
Super Admin and line-of-business heads set department and role policy, maintain model allow and block lists, and reuse policy templates instead of configuring each team from scratch.
Turn every request into an exportable audit record.
Real-time dashboards, full prompt history and traces, cost and token metering, and direct export to SIEM or CSV give Risk and Finance the evidence they need without asking IT for a report.
Built to sit inside a regulated environment.
Encryption, data residency controls, and tenant isolation keep prompts, files, and logs inside your environment. Folio3 is ISO 27001 certified as a company.
Runs on your hyperscaler, not a shared black box.
Deployed on your own cloud, Azure today with AWS and GCP ready, with managed model updates and a shared-IP, private-deploy model that keeps your data inside your tenant.
One platform. Seven layers of control, working together.
Each layer above is part of the same enterprise AI governance platform, so adding a new team, model, or agent does not mean adding a new tool to manage.
Control the moments that create risk.
Instead of relying on after-the-fact monitoring, AI Guardian applies identity, content, data, model, and budget rules while the request is happening.
Shield sensitive data before LLM ingress.
Automatically detect and mask IBANs, National ID numbers, phone numbers, financial details, and confidential content in prompts and multi-page attachments before data reaches the model.
- Prompt and multi-page file redaction
- Sanitized document previews before transmission
- Identity-attributed policy decisions and logs
Keep business AI on-domain and compliant.
Prevent misuse of organization-funded AI by declining off-domain requests and applying content controls that reflect corporate policy and ethics requirements.
- Context-aware off-domain restrictions
- Content moderation and discriminatory-content shields
- Rules applied consistently across models and agents
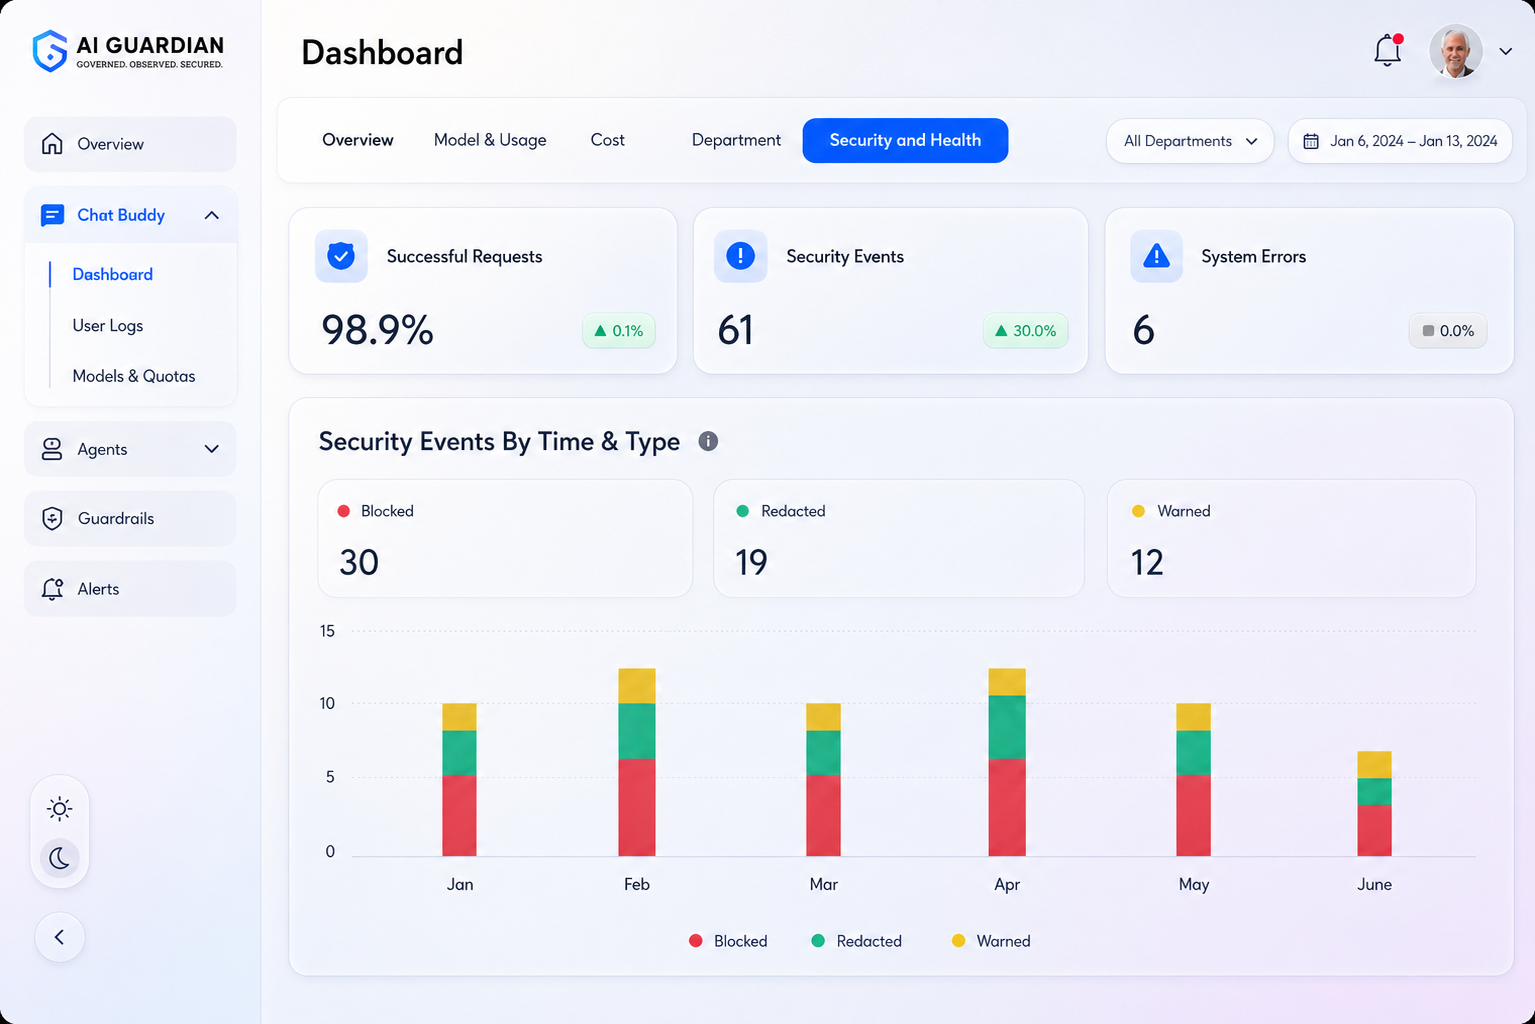
Match model power to role and budget.
Set monthly spend caps, token quotas, and model permissions by department or user role so high-consumption models are reserved for the work that warrants them.
- Department and role-level monthly caps, applied to everyone in the role at once
- Role-based model availability
- Cost and token traces at request level
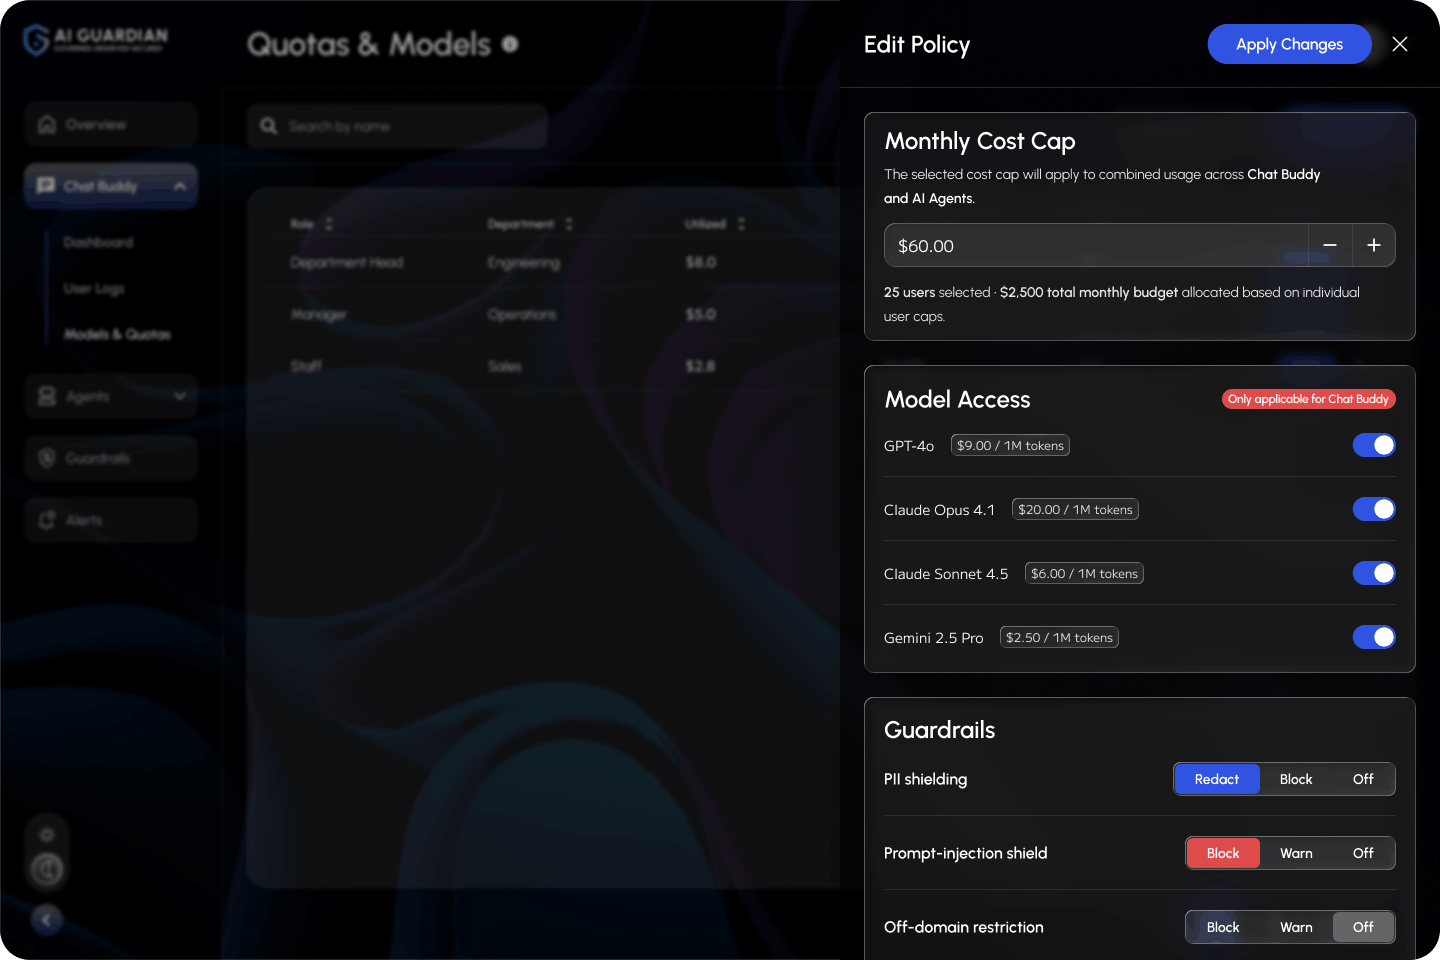
Stop Paying Frontier-Model Prices for Routine Work.
AI Guardian can govern model access by role and workload, so simple tasks use cost-efficient models while advanced reasoning is reserved for work that actually needs it.
One expensive model gets used for everything.
When organizations cannot see which models employees use for which tasks, low-complexity work can consume the same premium model capacity as high-value analysis and reasoning.
Match model capability to the work being done.
Role-based access, workload rules, approved model sets, and spend controls help route routine work toward lower-cost options while preserving premium models for complex reasoning, analysis, and high-impact workflows.
Example blended AI spend
Example only — actual savings depend on workload mix and model pricing.Microsoft guidance recommends matching model capability to requirements, restricting access to approved models, and controlling usage patterns to avoid unnecessary AI spending.
View Microsoft governance guidanceThe ≈30% savings figure and 100-to-25 task example above are example AI Guardian scenarios, not Microsoft benchmarks or guaranteed savings. Actual results depend on workload complexity, model mix, token usage, pricing, routing rules, and user behavior.
Move from basic chat to governed multi-agent work.
AI Guardian is not only a proxy for prompts. It can run fixed, repeatable workflows for routine processes, or plan a response dynamically when a request does not fit a template, orchestrating specialized agents, company knowledge, and business actions under the same governance layer.
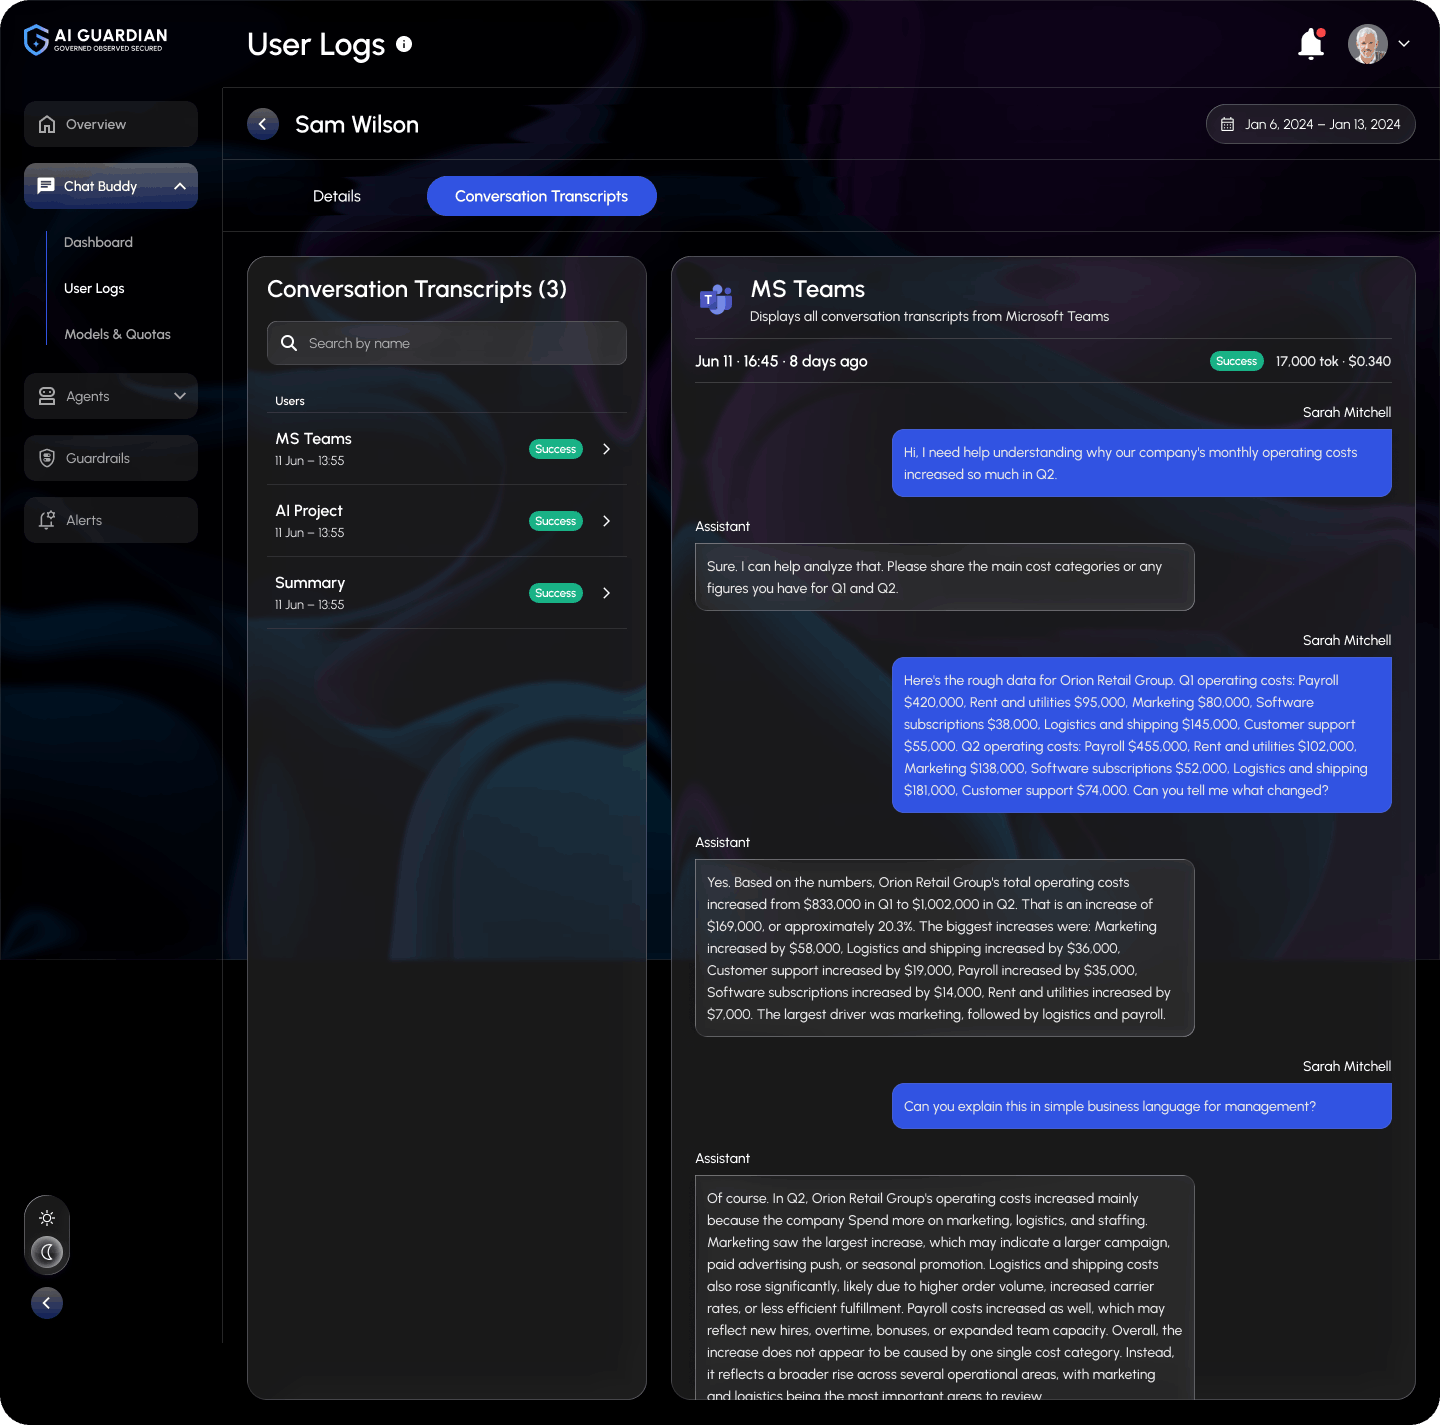
@ChatBuddy approve-invoice
Review the attached vendor invoice against procurement policy and the associated purchase order.
Reject the invoice. It includes an unlisted charge of $1,200 that is not listed on the Purchase Order and lacks written procurement approval.
AI governance software that gives every decision-maker the right level of control.
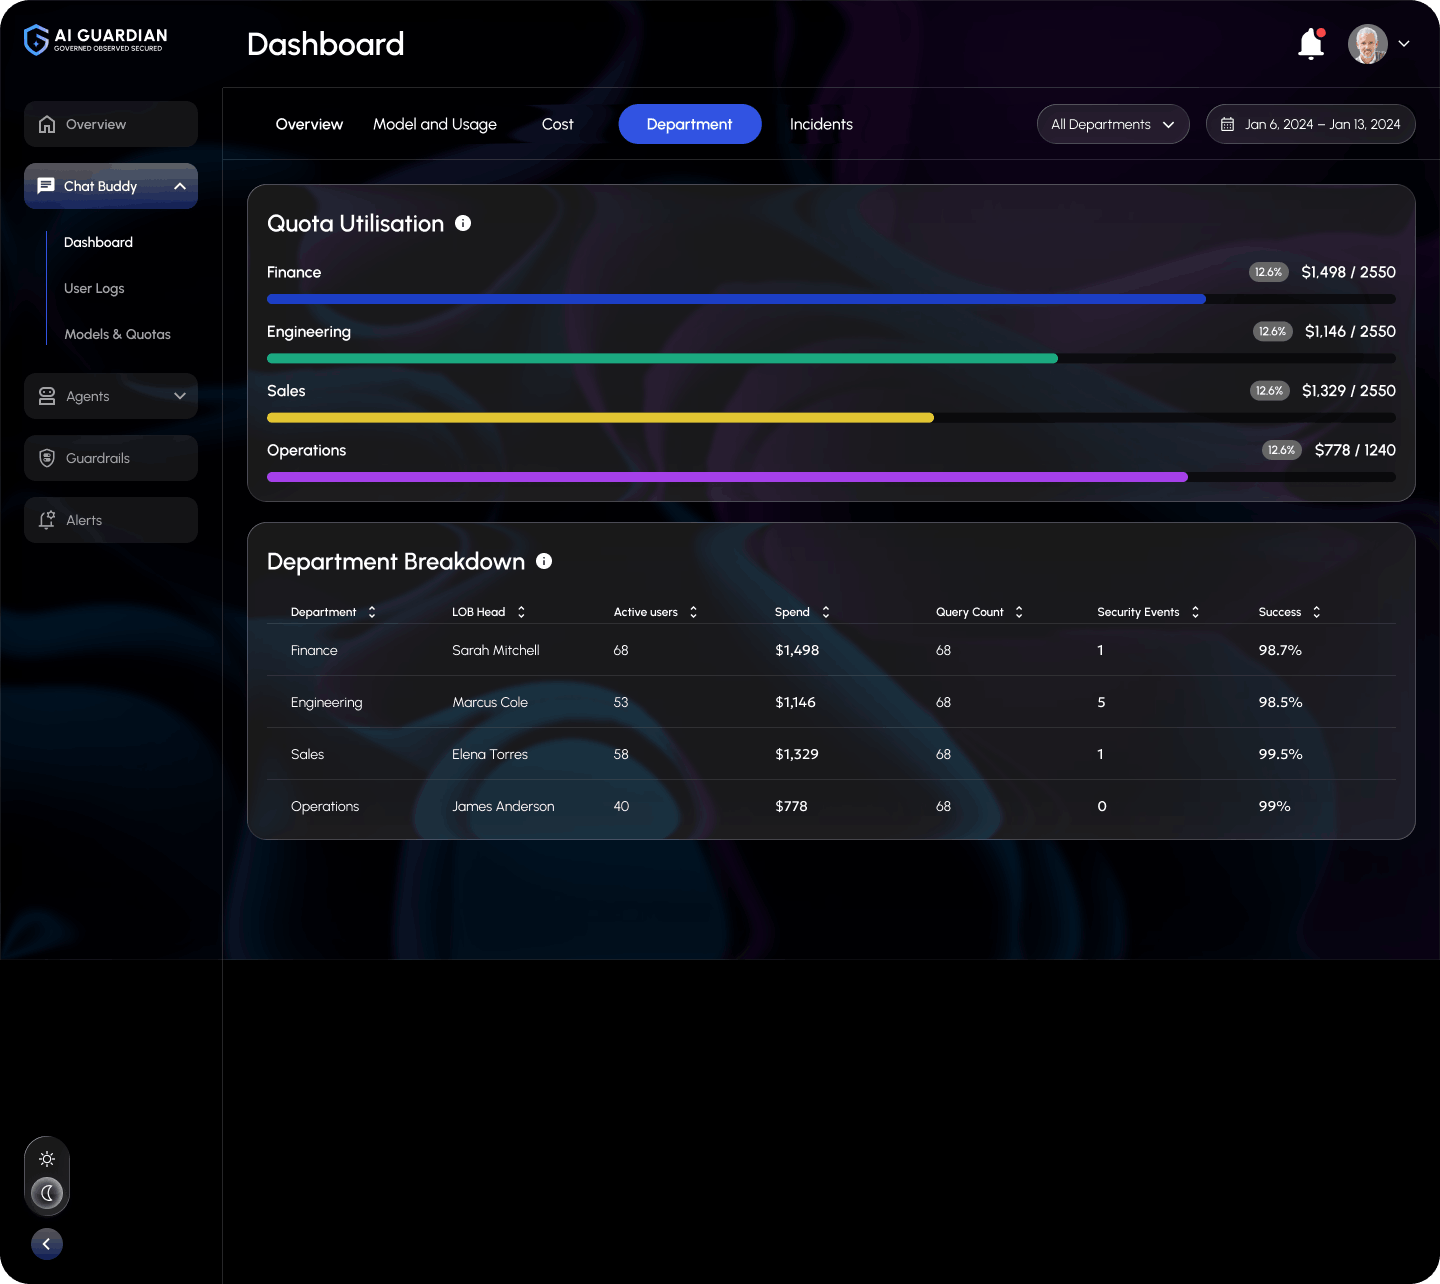
Department heads manage local quotas and model access. Risk and executive leadership see organization-wide usage, spend, blocked events, and identity-attributed audit history, with HRIS-driven sync keeping roles and access current automatically.
Local operational control
Set quotas, dollar caps, model availability, and monitor active departmental users.
Organization-wide evidence
See spend, security events, model distribution, user history, and complete audit traces.
How AI Guardian supports EU AI Act, NIST AI RMF and ISO/IEC 42001
AI Guardian supports evidence for these frameworks by enforcing policy at runtime and recording every decision. It does not replace the assessments, documentation, and human oversight each framework also expects.
EU AI Act: evidence for logging, monitoring, and controlled use.
Obligations depend on whether you act as a provider or a deployer and on each system's risk class, and they apply most fully to high-risk systems. For AI use that runs through AI Guardian, these are the duties it supports evidence for.
| Requirement | What AI Guardian does | Evidence it supports |
|---|---|---|
| Record-keeping and logs (Articles 12 and 26) | Logs every request with user, role, department, model, policy decision, tokens, and cost. | Identity-attributed logs kept in your own cloud tenant, exportable to SIEM or CSV |
| Use in line with instructions and approved purposes (Article 26) | Applies role and department policy, model allow and block lists, and off-domain blocking before any model call. | Records of which models each role may use, plus every blocked or rerouted request |
| Monitoring system operation (Article 26) | Shows usage, spend, blocked events, and security events in real-time dashboards. | Time-stamped usage and event history for risk and executive review |
| Human oversight (Article 14) | Not a product feature. Oversight roles and review steps are designed in your own process. | Outside AI Guardian's scope |
NIST AI RMF: evidence across Govern, Map, Measure, and Manage.
The NIST AI Risk Management Framework is voluntary and organizes AI risk work into four functions. AI Guardian supplies operational evidence for each one, and the risk decisions stay with your team.
| Requirement | What AI Guardian does | Evidence it supports |
|---|---|---|
| Govern: policies, roles, and accountability | Super Admin and line-of-business roles set policy by department and role, using reusable policy templates. | Documented policy sets with a named owner for each department |
| Map: context of AI use | Records which users, departments, models, and agents are in use, and for which tasks. | Usage context for AI that runs through AI Guardian; AI used elsewhere needs discovery tools |
| Measure: track risks and performance | Meters usage, cost, tokens, blocked events, and security events per user and department. | Exportable metrics over time |
| Manage: treat and monitor risks | Redacts PII before model ingress, blocks off-domain requests, routes to approved models, and enforces spend caps. | A logged record of every control decision |
| Model testing for bias and drift | Not covered. Model-level testing needs separate tooling. | Outside AI Guardian's scope |
ISO/IEC 42001: records your AI management system can use.
ISO/IEC 42001 certification applies to an organization's AI management system, not to a software product. AI Guardian supplies operational records that the system's controls and internal audits can draw on.
| Requirement | What AI Guardian does | Evidence it supports |
|---|---|---|
| AI policy (Annex A.2) | Applies policy templates and role-based rules consistently across departments, models, and agents. | Evidence that written AI policy is enforced in practice |
| Use of AI systems (Annex A.9) | Limits each role to approved models and tasks, with quotas and off-domain blocking. | Allow and block records plus blocked-request logs |
| Event logs (Annex A.6.2.8) | Keeps an identity-attributed trace for every request, including requests made by agents. | Structured, exportable event logs |
| Monitoring and measurement (Clause 9.1) | Dashboards and exports cover usage, spend, and policy events by department. | Inputs for internal audits and management reviews |
| AI system impact assessment (Annex A.5) | Not covered. Impact assessments are run inside your management system. | Outside AI Guardian's scope |
Start with shadow AI. Expand the same platform when you are ready.
The scope of governance widens over time, but it is the same control plane at every stage, so nothing gets re-bought, re-integrated, or re-governed as you extend it.
Control shadow AI
- Give every employee one approved way to use AI.
- Gain enterprise-scale visibility, control, and cost management over usage from day one.
- Replace personal-account AI use with a governed alternative.
Govern your own agents
- Agents built in Foundry or Copilot Studio register with AI Guardian.
- They run behind the same control plane without a line of their code changing.
- Identity, guardrails, and audit trail apply automatically.
Govern bought and BYO agents
- Knowledge agents grounded in your own content join the same registry.
- Third-party agents that act inside your existing tools through MCP are governed the same way.
- No separate policy layer for purchased tools.
The platform for all AI
- Workflows, future agents, and knowledge systems plug into the same plane.
- One policy model, one audit trail, and one cost view across every AI system in the business.
- Whatever comes next runs under the same enterprise AI governance platform.
Connects to the tools your teams and agents already use.
AI Guardian sits between people, agents, and models, so it plugs into the workplace, cloud, identity, and security systems already in place.
Microsoft Teams
Employees ask questions and upload files inside Teams, and SSO matches each user to their role, department, and policy set.
Slack
The same governed access, redaction, quotas, and audit trail for teams that work in Slack.
Azure
Deploys inside your own Azure tenant today, with AWS and GCP ready, so prompts and logs stay in your environment.
AI Foundry
Agents built in Foundry register with AI Guardian and run behind the same control plane without a line of their code changing.
Copilot Studio
Copilot Studio agents register with AI Guardian, and identity, guardrails, and audit trail apply automatically.
HRIS sync
HRIS-driven sync keeps roles and access current automatically as people join, move, or leave.
SIEM export
Prompt history, traces, and cost and token metering export directly to your SIEM or as CSV.
MCP
Third-party agents that act inside your existing tools through MCP are governed the same way as every other request.
A Clear Investment to Launch and Scale.
Start with a one-time implementation investment, then continue with a predictable quarterly AI Guardian platform license.
Covers the implementation phase required to align, configure, deploy, validate, and prepare AI Guardian for go-live in your environment.
Ongoing quarterly licensing for continued use of the AI Guardian platform after the initial implementation and launch.
Final commercial terms may vary based on implementation scope, organizational complexity, integrations, deployment requirements, and licensing needs.
From Alignment to Deployment in Days.
A focused two-phase rollout aligns this enterprise-ready AI governance framework software to your policies, users, controls, and cloud environment before go-live.
Requirements & Alignment
2–4 Hour SessionsUnderstand your business, governance needs, and implementation scope.
- Review AI policies, governance, compliance, and regulatory requirements.
- Map LOBs, teams, organization hierarchy, and priority use cases.
- Define guardrails, model access, and policy requirements.
- Identify user roles, permissions, and approval boundaries.
- Align budgets, quotas, reporting needs, and governance ownership.
Configure, Deploy & Go Live
4–5 Business DaysConfigure AI Guardian to your requirements and deploy it in your environment.
- Configure the AI Guardian platform and organization hierarchy.
- Implement guardrails, policies, roles, and permissions.
- Set model access, budgets, quotas, and usage controls.
- Customize dashboards, reporting, and administrator views.
- Deploy inside your tenant and validate connectivity and configurations.
- Run smoke testing, go live, and hand over operational controls.
Timing may vary based on organizational complexity, number of LOBs, policies, integrations, and security requirements.
Govern AI Around the Work People Actually Do.
AI Guardian can sit across industries and business functions to give employees approved access to models, agents, company knowledge, and business actions while applying the right identity, data, policy, model, cost, and audit controls.
Where AI Guardian fits first.
Govern document analysis without exposing sensitive financial data.
Analysts can review policies, agreements, reports, and internal knowledge through approved AI while sensitive identifiers are masked, model access is controlled, spend is governed, and activity remains attributable to the user.
Give administrative teams governed access to AI for sensitive workflows.
Operations teams can use approved AI for internal documents, procedures, summaries, and knowledge access while identity, sensitive-data protections, model permissions, and usage controls remain consistently enforced.
Use AI for contract and policy work without losing governance.
Legal and compliance teams can analyze internal policies, contracts, and supporting documents through approved models while AI Guardian applies document protection, role-aware access, off-domain restrictions, and traceable activity.
Make employee AI useful without opening unrestricted model access.
HR teams can use AI for policy questions, internal knowledge, drafting, and routine employee-support tasks while access is limited by role, approved model, department, quota, and organizational policy.
Review vendor documents with governed agents and company policy context.
Procurement teams can compare agreements, invoices, and vendor information against internal policy using approved agents and knowledge while AI Guardian preserves the same identity, redaction, model, budget, and audit controls.
Replace scattered shadow AI with one governed employee access layer.
IT and Security can centralize approved model and agent access, define role and department policies, monitor usage and spend, block prohibited activity, and retain identity-attributed evidence across employee AI interactions.
One governance layer. Different rules for different work.AI Guardian is designed to apply controls by user, role, department, model, agent, and business context instead of forcing every team into the same AI access pattern.
Book an AI Governance ConsultationHow AI Guardian compares with other AI governance tools.
Developer gateways route traffic, point tools filter prompts, and documentation-led platforms record policy. Each tab shows where a runtime control plane differs.
More than an API gateway. More than a prompt filter.
AI Guardian combines the employee workplace, security enforcement, agent orchestration, spend governance, and executive visibility inside one control plane. Most developer AI gateways stop at routing; an enterprise grade AI gateway solution has to cover all five.
| Capability | Traditional developer gateways | Point security tools | AI Guardian control plane |
|---|---|---|---|
| Primary design focus | API routing for developers | Keyword prompt filtering | Business-ready governed workplace |
| Employee workplace | Requires custom UI | No native interface | Teams, Slack & Web Apps |
| PII & document redaction | Basic text filters | Simple regex masking | Prompt & multi-page file masking |
| Multi-agent teaming | Single-model proxy | Not supported | Multi-agent orchestration |
| Off-domain enforcement | Unrestricted query types | Basic blocking | Contextual task rejection |
| Executive governance | Technical API logs | Security alerts only | CRO & department dashboards |
Business-ready governance Azure leaves for IT to build.
AI Guardian is built Azure-first and closes the gap between what Azure ships natively and what a business-owned AI governance solution needs to run day to day.
| Business need | Native Azure AI tooling | AI Guardian control plane |
|---|---|---|
| Department-managed governance | Left for IT to manage | Business-owned AI governance |
| Identity-driven access | HRIS integration for identity only | HRIS-integrated AI governance |
| Dashboards and reporting | Technical platform monitoring | Business dashboards, insights & audit reports |
| Document workflows | Sensitive-content detection only | End-to-end governed document workflow |
| Vendor flexibility | Limited to Azure ecosystems | One governance layer across every AI vendor |
| Consistency across deployments | Features vary by deployment | Consistent AI capabilities everywhere |
Runtime governance vs documentation-led governance.
Documentation-led AI governance tools record policies, inventories, and assessments. Runtime governance enforces those policies on each request as it happens. Most programs need both, and the table shows where each approach is strongest.
| Capability | Documentation-led governance | AI Guardian runtime governance |
|---|---|---|
| When controls act | At review cycles and before deployment | On every request, before data reaches a model |
| Policy | Written policies and attestations | Policy enforced by role, department, and model |
| Sensitive data | Depends on employee training | PII and file redaction before model ingress |
| Approved models | Approved-tool lists in documents | Model allow and block lists applied at request time |
| Audit evidence | Assessments and questionnaires compiled by hand | Identity-attributed logs generated automatically |
| Risk and impact assessments | Core strength | Supplies usage evidence; assessments run elsewhere |
Explore the controls behind confident AI adoption.
From discovering unauthorized AI use to managing agents and model access, explore the governance capabilities that help your organization stay in control.
AI Risk Management Software
Identify, assess, and monitor AI risks with centralized visibility into usage, controls, and governance decisions.
Explore risk managementAI Guardrails Platform
Apply policies and safeguards to AI interactions to reduce sensitive-data exposure and unsafe outputs.
Explore AI guardrailsEnterprise LLM Gateway
Route model requests through a unified layer for access control, monitoring, and spend management.
Explore the LLM gatewayAI Agent Governance
Establish oversight for autonomous agents, including what they can access, which actions they take, and how activity is audited.
Explore agent governanceShadow AI Detection Software
Discover AI tools and activity outside approved channels so teams can address unmanaged usage and associated risks.
Explore shadow AI detectionQuestions teams ask before rollout.
What is AI governance software?
AI governance software helps an organization discover the AI systems it uses, assess their risk, set and enforce policy, and keep audit evidence across the AI lifecycle. AI Guardian covers the runtime layers of that work: it enforces identity, data protection, policy, model routing, and cost caps on every request that passes through it, governs registered agents, and keeps identity-attributed audit records. Discovering AI used outside that path, formal risk assessments, and model-level bias or drift testing need separate tools, and AI Guardian can feed them evidence through SIEM or CSV export.
What is AI Guardian?
AI Guardian is an enterprise AI control plane and governed workplace. It gives employees approved access to models, agents, company knowledge, and business actions while enforcing identity, security, PII protection, model routing, cost caps, and audit logging.
How does AI Guardian differ from a developer API gateway?
Standard AI gateways focus primarily on API routing and developer metrics. AI Guardian adds a complete employee workplace, multi-page PII redaction, multi-agent orchestration, and executive governance for department heads and risk leadership.
Can AI Guardian run inside our private cloud?
Yes. AI Guardian is designed for private deployment within enterprise cloud environments such as Azure, AWS, or GCP, aligned with network security, encryption, data residency, and tenant isolation requirements.
How does AI Guardian handle sensitive files and prompts?
The platform intercepts prompts and uploaded documents in real time. Sensitive identifiers and confidential details can be redacted before the request is routed to a model provider.
Can we govern AI agents we already built or purchased?
Yes. Third-party and custom internal agents can plug into the agent registry so requests inherit the same identity controls, data redaction, spend tracking, and audit logging used for standard prompts.
How does off-domain query blocking save money?
By preventing organization-funded LLM capacity from being used for non-business tasks, teams can keep AI spend aligned to approved business use cases and make consumption more predictable.
What is shadow AI and how does AI Guardian reduce it?
Shadow AI is employee use of AI tools that IT and security have not approved. AI Guardian gives employees one approved path in Microsoft Teams, Slack, the web app, or mobile, so each request is tied to their identity, checked for sensitive data, routed to an approved model, and logged instead of going to a personal account.
Which models and channels does AI Guardian work with?
Employees reach AI Guardian through Microsoft Teams, Slack, the web app, or mobile. Each request is routed to the approved LLM for that user's role and task, based on policy, departmental quotas, and model permissions. The approved model set is configured with your team during implementation.
How is AI Guardian priced?
AI Guardian has two costs: a one-time implementation from $15K and a quarterly platform license from as low as $8K per quarter. Final terms depend on implementation scope, organizational complexity, integrations, deployment requirements, and licensing needs, and Folio3 confirms them with you during an AI governance consultation.
How long does an AI Guardian rollout take?
Rollout runs in two phases. Requirements and alignment sessions of 2 to 4 hours review your policies, teams, roles, budgets, and priority use cases. Configuration, deployment inside your tenant, testing, and go-live then take 4 to 5 business days, depending on organizational complexity, number of LOBs, policies, integrations, and security requirements.
Your employees will use AI either way. Choose the environment you can govern.
Move AI out of the shadows and onto a platform your organization owns, governs, measures, and can defend with identity-attributed audit evidence.
Book an AI Governance Consultation
